Executive Summary and Group Overview
The Gentlemen is a Ransomware-as-a-Service (RaaS) operation that emerged in mid-2025 and transitioned to a full affiliate model in September 2025. Within its first year of operation it became one of the two highest-volume RaaS programs globally by claimed victim count, responsible for an estimated 10% of all publicly tracked ransomware incidents in early 2026. In June and July 2026 it briefly overtook Qilin for the top position by monthly leak-site volume before Qilin retook first place in August with a record month; The Gentlemen is the second most active RaaS program of 2026 (Unit 42) and the two-leader pattern with Qilin, both at roughly double every other group's volume, has held since May 2026. The group is characterized by a generous 90/10 revenue split favoring affiliates, a Go-based encryptor with aggressive self-propagation capability, and a deliberate policy of excluding Commonwealth of Independent States (CIS) targets, consistent with Russian-speaking origin. Microsoft Threat Intelligence tracks the operator cluster as Storm-2697; the malware family is detected as Ransom:Win64/Gentlemen.A.
The group's operational data was partially compromised in May 2026 when internal Rocket.Chat communications and panel data were leaked and circulated on underground forums. Despite this OPSEC setback, the group continued active operations with no observable disruption to victim accumulation. In June 2026, investigative reporting by Brian Krebs identified the lead operator (handles hastalamuerte and zeta88) as Alexander Andreevich Yapaev, a 36-year-old from Izhevsk, Russia (CREDIBLE, single-source investigative attribution; see Section 09).
| Attribute | Detail |
|---|---|
| Common names | The Gentlemen, TheGentlemen, Gentlemen RaaS |
| Microsoft tracking | Storm-2697 (operator cluster); Ransom:Win64/Gentlemen.A (malware family) |
| Fortinet FortiGuard | "The Gentlemen Ransomware" (no internal codename published as of September 2026) |
| Palo Alto Unit 42 | "The Gentlemen (aka Storm-2697)"; formal profile published July 2026, no proprietary codename assigned. Unit 42 tracks Qilin as Spikey Scorpius and Akira as Howling Scorpius |
| Kaspersky (Securelist) | "The Gentlemen RaaS"; C and Go variant analysis plus custom Go-based backdoor |
| ESET | "The Gentlemen" (GentleKiller EDR-killer framework analysis) |
| IBM X-Force | "The Gentlemen" threat group (internal GUID: 688ac4f45c5a4791b8019a4d313594f7; no codename published) |
| Check Point Research | "The Gentlemen Ransomware-as-a-Service" (no additional family tag) |
| Halcyon | "The Gentlemen Ransomware Group" (no codename) |
| Trend Micro | "The Gentlemen ransomware" (no codename) |
| Cybereason | "The Gentlemen" (no codename) |
| Group-IB | "The Gentlemen" (no codename) |
| Operational model | Ransomware-as-a-Service with affiliate panel, custom build generator |
| Extortion mechanic | Double extortion (encryption + data publication threat); opportunistic triple extortion elements |
| Assessed jurisdiction | Russia / CIS region (CREDIBLE) |
| LE disruption status | None confirmed as of September 2026 |
| Lineage assessment | Splinter from Qilin ecosystem: founder ran Qilin affiliate crew ArmCorp, split after July 2025 payment dispute (CREDIBLE, multi-vendor) |

Lineage and Organizational Heritage
Multi-vendor consensus holds that The Gentlemen emerged from the Qilin ransomware affiliate ecosystem following a payment dispute, with experienced operators breaking away to found a new, independently branded RaaS. This is best characterized as a splinter or successor operation, not a rebrand: The Gentlemen operates under a distinct brand, distinct codebase (Go, not Qilin's Go variant), and distinct business model with a notably more generous affiliate split. Halcyon, IBM X-Force, and Ransom-ISAC all support this framing, and Unit 42's July 2026 profile (citing PRODAFT) states the operators were likely active months earlier as a Qilin affiliate crew known as ArmCorp. No vendor has formally assessed it as a direct rebrand. [1][4][5][7][19]
The split narrative is now documented in detail. On 2 July 2025 the lead operator, under the handle hastalamuerte, filed a public arbitration complaint on the RAMP forum alleging Qilin withheld roughly $48,000 in commission from a victim negotiation, and claimed Qilin's operators deleted the negotiation Tox history. The first Gentlemen sample appeared on VirusTotal on 17 July 2025 with the leak-site URL already hardcoded, indicating the departure was premeditated and the public dispute was the break point rather than the cause. [21]
| Vendor | Position | Confidence Applied |
|---|---|---|
| Halcyon | Formed after a payment dispute within the Qilin ecosystem; approximately 20-person core team; deliberately more attractive business model than predecessor | Credible |
| IBM X-Force | Emerged from Qilin ecosystem; distinct group with experienced operators; not a Qilin rebrand | Credible |
| Ransom-ISAC | Internal chats reference prior RaaS grievances consistent with Qilin; operator "zeta88" discussed payment disputes predating The Gentlemen's launch | Credible |
| Check Point Research | Distinct RaaS operation; Qilin lineage not formally assessed in published reporting | Not formally assessed |
| Microsoft (Storm-2697) | Financially motivated RaaS operator; Qilin lineage not referenced in published reporting | Not formally assessed |
| Group-IB | Positions within Russian-language RaaS cluster sharing infrastructure and tooling with Qilin and others; treats as distinct group | Credible (shared ecosystem) |
| Palo Alto Unit 42 (Jul 2026) | Operators likely active months earlier as Qilin affiliate ArmCorp, citing PRODAFT reporting; treats as distinct RaaS program | Credible |
| SOCRadar (May 2026) | hastalamuerte ran ArmCorp under Qilin; 2 July 2025 RAMP complaint over roughly $48,000; VirusTotal sample 17 July 2025 with hardcoded leak-site URL shows premeditated departure | Credible |
Operational Model
The Gentlemen began as a closed group in mid-2025 and transitioned to a full RaaS model with external affiliates in September 2025. [13][1] The group subsequently established an official partnership with BreachForums, a major cybercriminal marketplace, to recruit affiliates including penetration testers and initial access brokers. [1] The operator provides: a custom build generator panel producing multi-platform lockers; affiliate-specific Tox/Session IDs injected into ransom notes; and a data leak site for victim publication.
The core operator is identified in internal communications under the handle "zeta88," who manages the panel, conducts affiliate onboarding via Tox and Session, and sets revenue settlement arrangements. [3][7] Internal chats describe approximately 20 core personnel at the operational level. [4]
The 90/10 split and affiliate-owned wallet model are structurally significant for on-chain attribution: there is no single operator wallet to trace. Payment flows are highly fragmented across numerous affiliate wallets, consistent with what Halcyon describes as a "RaaS-as-SaaS" cash-out architecture. [4][16]
Recruitment is conducted via underground forum postings and the BreachForums partnership. The group targets affiliates with demonstrated intrusion skills, specifically penetration testers and initial access brokers capable of delivering high-value targets. Mass-spam operators are deprioritized in favor of skilled, targeted operators. [3][8] Basic technical vetting occurs before panel access is provisioned. [3]
Internal chats indicate preference for affiliates who can bring their own initial access or who have established relationships with IABs. This produces an affiliate pool oriented toward mid-market and enterprise targets rather than opportunistic volume attacks. [12]
- Initial demands: Low- to mid-eight-figure USD equivalent for large enterprises; scaled to perceived victim revenue and liquidity. [9]
- Discount range: 40-70% off initial ask documented in analyzed incidents. [9]
- Deadlines: Typically 5-10 days before publication threats escalate; some cases show staged partial data leaks as interim pressure. [6]
- Communication channels: Tox and Session IDs (affiliate-specific, injected at build time); sometimes email or Tor portal. [2][3]
- Operator involvement: Minimal during negotiations; affiliates run their own deals. Operator engages only in disputes or complex settlements. [3]
Standard (double extortion): Data exfiltration precedes encryption. Non-paying victims are named on the Tor-based leak site, with staged data publication (sample data first, full archive later). [2][6]
Opportunistic (triple extortion): Some affiliates have threatened DDoS or regulatory reporting (e.g., notifying the victim's regulator of a data breach) as additional pressure. These appear affiliate-driven and opportunistic rather than formalized RaaS policy. [5]
Technical Capabilities
| Platform | Language | Encrypted Extension | Notes |
|---|---|---|---|
| Windows | Go (Garble obfuscated) | .umc16h | Primary; self-propagating; per-file ephemeral key encryption |
| Linux | Go | TBD | Confirmed per IBM X-Force / Check Point |
| NAS / BSD | Go | TBD | Confirmed per IBM X-Force |
| ESXi | C | TBD | Separate C-based locker; targets virtual environments |
The Windows encryptor implements a hybrid cryptographic design documented by Microsoft: [1]
- Per-file ephemeral Curve25519 key pair: A unique ephemeral keypair is generated for each file. The ECDH shared secret between the ephemeral private key and the operator's embedded public key is used as the XChaCha20 key.
- XChaCha20 stream cipher: File content is encrypted using XChaCha20. The nonce is derived from the first 24 bytes of the ephemeral public key, making separate nonce storage unnecessary.
- File footer: The Base64-encoded ephemeral public key is appended to the encrypted file after the marker --eph--, along with a GENTLEMEN identification marker. Large files also include a speed flag marker indicating the chunk percentage used.
- Size-based strategy: Files under 1MB are fully encrypted. Files over 1MB are partially encrypted in three distributed chunks (default: 9% per chunk, ~27% total). Speed flags allow affiliates to set ultrafast (0.9%), superfast (3%), or fast (9%) modes.
| Vector | Assessment | Sources |
|---|---|---|
| FortiGate SSL-VPN exploitation / brute force | Primary vector per Raven File and Ransom-ISAC analysis; credential theft or exploitation of SSL-VPN configuration weaknesses | [8][7] |
| Infostealer-driven credentials | Hudson Rock describes this as the group's defining access model: large-scale infostealer log purchases providing VPN, RDP, and SaaS credentials at scale | [11] |
| Cisco VPN / edge device exploitation | Confirmed per Spanish-language reporting and Group-IB TTP analysis; credential reuse or appliance exploitation | [10] |
| RDP (compromised credentials) | Documented by FortiGuard as a key vector alongside VPN access | [6] |
| Phishing (credential harvesting) | Listed by FortiGuard; less prominent than VPN/infostealer vectors in DFIR case reporting | [6] |
| Initial access broker (IAB) purchases | Consistent with affiliate recruitment targeting IABs; internal chats show discussion of purchased access | [3] |
- Disables Microsoft Defender: PowerShell commands disable real-time monitoring, add exclusion paths, and exclude the full C:\ volume from scanning. [1]
- Deletes shadow copies: Both vssadmin and wmic are used to delete all Volume Shadow Copies. [1]
- Clears event logs: System, Application, and Security logs cleared via wevtutil. [1]
- Removes forensic artifacts: Prefetch files, Defender diagnostic logs, RDP logs, and PowerShell command history (PSReadline) deleted across all user profiles. [1]
- Process and service termination: Extensive target list including databases (MSSQL, MySQL, PostgreSQL, Oracle), backup software (Veeam, Acronis, Backup Exec), EDR agents, SAP, virtualization (VMware, Docker), Office apps, and Exchange. [1]
- Garble obfuscation: The Go binary is obfuscated with Garble to hinder static analysis and EDR detection. [1]
The encryptor establishes layered persistence via two independent methods: [1]
- Scheduled Tasks: Tasks named UpdateSystem (SYSTEM context) and UpdateUser (current user context) are created to relaunch the payload at startup. A separate task named gentlemen_system is used for privilege escalation during the encryption phase.
- Registry Run Keys: Values GupdateS (HKLM, device-wide) and GupdateU (HKCU, user-scoped) provide redundant autorun paths across privilege levels.
The most operationally distinctive feature of The Gentlemen encryptor is its self-propagation module, activated via the --spread argument. When enabled, the malware transforms from a single-host encryptor into a network worm that attempts deployment to every reachable host on the network simultaneously. [1]
Per Microsoft's analysis, the module executes 21 distinct remote execution operations per discovered target host across eight independent methods, each attempted regardless of prior success: [1]
| Propagation Method | Description |
|---|---|
| Remote file copy via C$ share | Stages payload on target's local C:\Temp via administrative share |
| PsExec (embedded or downloaded) | Three-stage PsExec execution: defense evasion blob, payload from SMB share, payload from local C:\Temp |
| WMIC process creation | Three commands via wmic.exe: defense evasion, then two payload executions |
| Scheduled tasks (user context) | Three tasks: DefU (evasion), UpdateGU and UpdateGU2 (payload from both paths) |
| Scheduled tasks (SYSTEM context) | Same three tasks replicated under SYSTEM account for higher privilege |
| Windows service creation | DefSvc, UpdateSvc, UpdateSvc2 services created and started on target |
| PowerShell remoting (WinRM / Invoke-Command) | Direct remote execution via Windows Remote Management |
| PowerShell WMI class (Win32_Process) | Alternative WMI path bypassing wmic.exe if binary is restricted |
The malware first creates a hidden SMB share (share$) on the infected host pointing to C:\Temp, enabling anonymous retrieval of the payload by target hosts. It also modifies firewall rules and enables network discovery services (fdrespub, fdPHost, SSDPSRV, upnphost) to maximize visibility into the network. On each target, it runs a defense evasion blob that disables Defender, turns off the Windows Firewall across all profiles, enables SMB1, and loosens LSA anonymous-access restrictions before executing the payload. [1]
| Phase | Tools / Techniques |
|---|---|
| Initial staging / C2 | SystemBC (SOCKS5 proxy and C2 tunneling); AnyDesk, WinSCP, PuTTY, AnyDesk, RustDesk |
| Discovery | Advanced IP Scanner, Nmap, net commands |
| Credential access | Domain credential dumping; ICACLS for permission manipulation; stolen VPN/infostealer credentials |
| Lateral movement | PsExec, WMI, PowerShell remoting, Windows services; RDP; WinRM |
| Exfiltration | SystemBC-tunneled exfiltration; WinSCP |
| Persistence (hands-on-keyboard) | Scheduled tasks, Registry Run keys, Windows services |
The Gentlemen enforces an explicit policy prohibiting attacks on organizations in Russia and other CIS countries. FortiGuard reports this as an operator-level policy; Group-IB notes it as consistent with Russian-language RaaS norms. Some technical analyses reference locale or language checks in the encryptor, though binary-level detail on the CIS exclusion mechanism has not been published as of September 2026. [6][10]
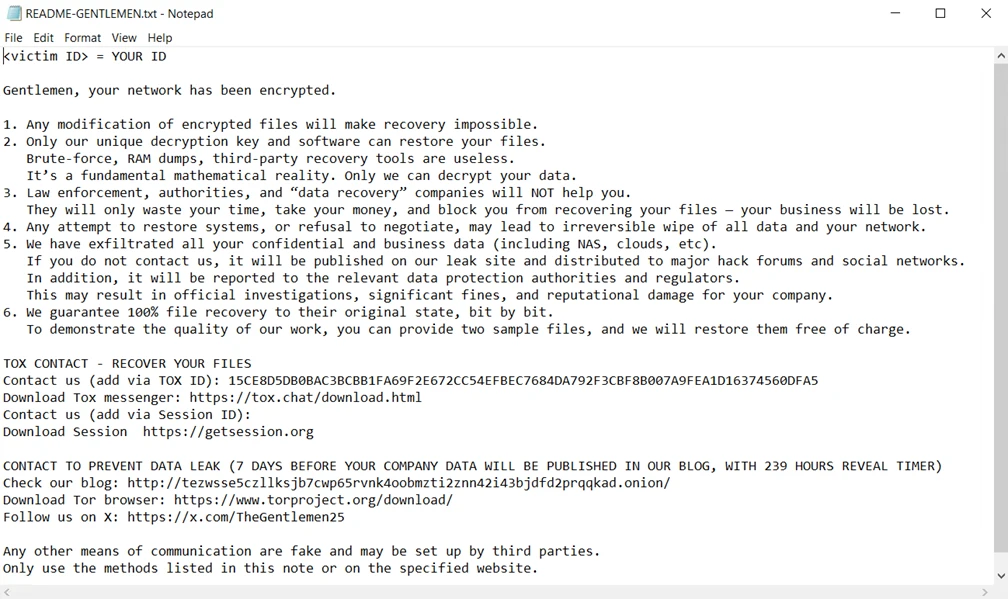
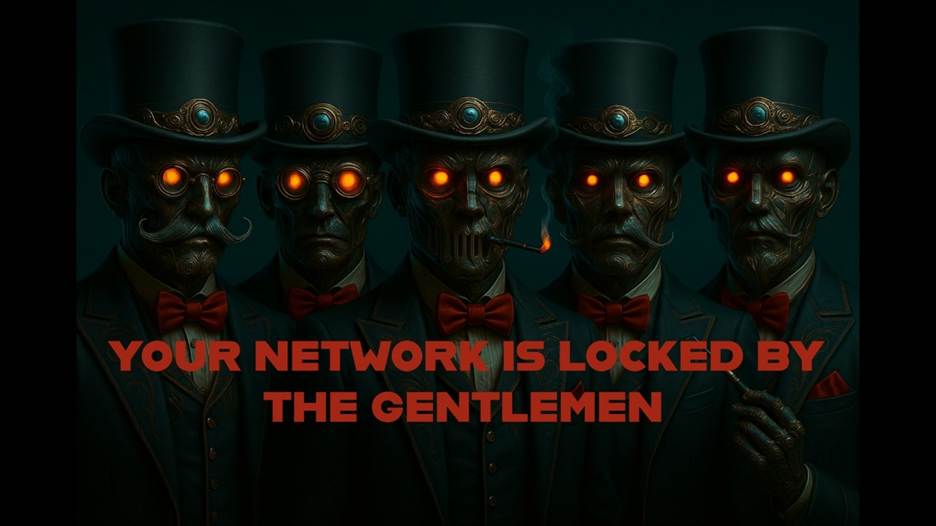
Note filename: README-GENTLEMEN.txt (excluded from encryption target list). Contents: victim-specific identifier, affiliate Tox and Session contact IDs, Tor portal link, payment instructions in cryptocurrency, threat of data publication if unpaid, and a warning against third-party decryption attempts. Tone is pragmatic and business-oriented. The note is dropped in each scanned directory during traversal. [1][2]
Defensive Mapping
This section translates reporting into defender action items. No government advisory as of July 2026. Sourced from vendor reporting (Trend Micro, Check Point Research, Microsoft, ESET, Huntress). The Gentlemen is a fast-growing 2025-era RaaS with a self-propagating Go encryptor; confidence is Credible. Rows are rated Credible based on source. Techniques reflect documented tradecraft; no single intrusion uses all of them.
| Technique | Tactic | Usage | Defender Action |
|---|---|---|---|
| T1190 Exploit Public-Facing Application | Initial Access | Exploits exposed applications and edge devices for entry | Patch KEV-listed edge CVEs; remove management interfaces from the internet |
| T1484.001 Domain Policy Modification: Group Policy Modification | Privilege Escalation / Defense Evasion | Abuses Group Policy Objects and a custom deploy_gpo.ps1 to push payloads domain-wide and create fake "update" policies that disable Defender | Alert on unexpected GPO creation and edits; restrict who can link GPOs; monitor for gpupdate /force from non-admin hosts |
| T1562.001 Impair Defenses: Disable or Modify Tools | Defense Evasion | Bring-your-own-vulnerable-driver and the custom GentleKiller EDR-killer framework (ESET); Expel reports a suspected zero-day exploit used to disable EDR | Enable Microsoft vulnerable-driver blocklist; tamper-protect EDR; alert on driver-load anomalies |
| T1570 Lateral Tool Transfer | Lateral Movement | Distributes payloads via the NETLOGON share from domain controllers | Monitor NETLOGON/SYSVOL for unexpected executables; alert on new files on domain controllers |
| T1059.001 Command and Scripting Interpreter: PowerShell | Execution | Uses PowerShell (deploy_gpo.ps1) for rapid GPO-based propagation | Constrained-language mode; script-block logging; alert on policy-manipulation scripts |
| T1486 Data Encrypted for Impact | Impact | Self-propagating Go encryptor targeting large enterprises and critical infrastructure | Deploy EDR ransomware-behavior detection; segment to contain self-propagation; immutable offline backups |
Curated for detection and hardening value; not an exhaustive mapping.
Financial Infrastructure
Ransoms are demanded primarily in Bitcoin; some affiliates may accept additional cryptocurrencies at their discretion. The affiliate-owned wallet model means payment goes directly to the affiliate's wallet, with the operator's 10% settled via internal arrangement afterward. This architecture produces no single canonical operator wallet and significantly complicates on-chain attribution. [16][7]
As of September 2026, no TRM Labs, Chainalysis, or Elliptic study specifically mapping The Gentlemen's on-chain fund flows has been published. This is an active intelligence gap. The following is derived from general RaaS-ecosystem reporting and internal leak analysis:
Total revenue extracted by The Gentlemen is not yet clearly quantified in public sources. Single-source estimates characterize tens of millions of USD equivalent in 2025-2026 based on partial payment observations and average demand sizes, but these carry low confidence. The combination of high victim volume (420+ claimed), mid-to-high-value targeting, and a generous affiliate split suggests a rapidly growing total revenue figure. [16]
As of September 2026, no OFAC designation, EU sanctions listing, or equivalent action specifically naming The Gentlemen, its wallets, or any identified individual in the operator cluster has been publicly reported, despite the June 2026 public identification of the lead operator. The typical lag between LE intelligence gathering and sanctions action means this gap is expected rather than indicative of reduced threat. [17]
Victim Profile and Targeting
Targeting is assessed as primarily opportunistic, driven by affiliate access availability rather than deliberate pre-selected sector strategy. Sectors documented across DFIR cases and vendor reporting: [1][6][12]
| Sector | Evidence Level | Notes |
|---|---|---|
| Education | Confirmed (Microsoft) | Observed in Microsoft's documented impact set |
| Healthcare | Confirmed (Microsoft / FortiGuard) | No documented exclusion; healthcare not protected |
| Transportation / Logistics | Confirmed (Microsoft) | Documented in Microsoft case analysis |
| Financial Services | Confirmed (Microsoft) | Documented in Microsoft case analysis |
| Manufacturing / Industrial | Confirmed (Unit 42) | Largest single sector: 103 of 580 victims through 7 Jul 2026; also noted by S-RM and SOC Prime in Asia-Pacific and Europe |
| Energy / Government / IT | Credible (FortiGuard) | Listed among targeted sectors; individual cases not named |
Victims span all major global regions with particular concentration in Asia (Japan, South Korea, Southeast Asia), North America, and Europe. CIS-region organizations are systematically excluded per group policy. [1][6][9]
Internal chats show affiliates focusing on organizations with high perceived ability to pay, using revenue or employee count as heuristics. Mid-market and large enterprises are prioritized; some affiliates explicitly avoid very small targets as uneconomical. [7]
The 1,570+ victim count from the SystemBC C2 compromise includes a large number of small and mid-sized organizations appearing as partial or failed intrusions, suggesting wide scanning and triage with selective escalation to full deployment against higher-value targets. [16][17]
Individual victim names disclosed by The Gentlemen on its leak site are not reproduced here. Vendor briefings reference large manufacturing, energy, and healthcare firms by sector but avoid naming due to legal exposure. Open-source lists of named enterprises remain partial, scattered across sources, and predominantly single-sourced. Analysts requiring named victim lists should consult ransomware.live directly.
Law Enforcement and Regulatory Response
As of September 2026, no publicly known arrests, indictments, or named individual charges linked to The Gentlemen have been issued by any Western or CIS law enforcement authority, despite the June 2026 public identification of the lead operator by investigative reporting. The typical intelligence-gathering phase preceding overt enforcement action means this gap is consistent with normal LE timelines rather than indicative of investigative disinterest, though the group now sits alongside Qilin, Akira and DragonForce in the zero-enforcement-exposure tier of top-volume operations. [17][20]
No coordinated public LE takedown (FBI/Europol seizure banners, domain seizures, key escrow releases) has been announced against The Gentlemen infrastructure. The SystemBC C2 compromise and Rocket.Chat internal data leak analyzed by KELA and Ransom-ISAC are products of private-sector research and/or adversarial insider activity, not formal LE operations. [3][17]
No OFAC, EU, UK, or equivalent financial sanctions specifically naming The Gentlemen, its wallets, or identified individuals in the group have been announced as of September 2026. [17]
No dedicated multi-agency joint advisory (comparable to the LockBit or Hive advisories from FBI/CISA/NCSC) has been issued against The Gentlemen as of September 2026. The group is referenced in general ransomware-threat advisories and sectoral alerts but has not yet triggered a named advisory product from Five Eyes partners. [5]
CISA, FBI, and partner agency advisories on ransomware in general remain applicable given the group's TTPs (edge device exploitation, VPN credential abuse, double extortion). Specific IoC packages for The Gentlemen are available via Microsoft Defender XDR threat analytics (Storm-2697 / Gentlemen tool profile). [1]
Attribution and State Nexus
Multiple converging indicators support attribution to Russian-speaking operators in the CIS region: [1][6][10]
- CIS exclusion policy: Explicit prohibition on targeting Russian and CIS organizations, enforced at the operator policy level. This is the single strongest jurisdictional indicator and is consistent across all vendor assessments.
- Language: Internal Rocket.Chat communications analyzed by KELA are Russian-language. [3]
- Ecosystem positioning: IBM X-Force and Group-IB position The Gentlemen within a cluster of Russian-language RaaS operations sharing language, tooling preferences, and no-CIS policies. [5][10]
- No-CIS behavioral norm: The CIS exclusion pattern is a known proxy indicator for Russian-nexus actors operating under de-facto safe harbor: criminal activity tolerated by Russian authorities as long as it remains directed outward. [4]
No vendor or government publication as of September 2026 provides direct evidence of FSB, SVR, or GRU control, tasking, or operational coordination with The Gentlemen. The group is assessed as financially motivated criminal rather than state-directed. [1][4]
As with other top-tier Russian-language RaaS operations, The Gentlemen likely operates under de-facto non-prosecution safe harbor in CIS territory, consistent with Russia's documented pattern of tolerating outward-facing cybercriminal activity. This is an analyst inference based on structural patterns, not a confirmed intelligence finding. [4]
The core operator is identified in internal communications by the handles "zeta88" and "hastalamuerte" (the latter used on RAMP, including for the July 2025 Qilin arbitration complaint, and previously as head of the ArmCorp Qilin affiliate crew). On 10 June 2026, Brian Krebs, drawing on Check Point and Intel 471 research linking email addresses, phone numbers, and social media profiles, identified the operator as Alexander Andreevich Yapaev, a 36-year-old from Izhevsk, Russia, who has listed a professional role in B2B marketing at Uralenergo Udmurtia. Confidence: CREDIBLE (investigative attribution, methodologically documented, but single-outlet and without law enforcement confirmation). The May 2026 leak also surfaced additional internal handles (Kunder, qbit, JeLLy, Protagor, Bl0ck, Wick, quant, donpakto), none attributed to real identities. [3][5][20][21]
Trajectory Assessment
In May 2026, partial internal chat logs (Rocket.Chat backend), panel data, and images tied to The Gentlemen were leaked and advertised on underground forums. KELA, Ransom-ISAC, and Check Point analyzed the dataset. The leak revealed internal arguments about target selection, payment disputes, quality of initial access, and OPSEC practices. The likely cause was insider betrayal or compromise of admin infrastructure. [2][3][7][8]
Despite this OPSEC setback, new victim claims continued appearing on The Gentlemen's leak site through May 2026, and no operational pause has been documented. The group appears resilient to the leak, consistent with a distributed affiliate model where individual compromise of operator communications does not halt affiliate operations. [9]
As of early September 2026, there are no credible signals of an active rebrand. Notably, neither the May 2026 internal leak nor the June 2026 Krebs identification of the lead operator produced an operational pause or brand change. The post-identification record is worth stating precisely: Krebs published the Yapaev identification on 10 June 2026, and the two months that followed were the brand's two biggest on record (118 victims in June, 136 in July, internal collection), the exact period in which it overtook Qilin for the monthly top slot, before settling to 115 and second place in August. No arrest, no indictment, no sanctions, and no observable operational change followed the naming. [CONFIRMED, internal collection] [ANALYST INFERENCE] Public attribution without jurisdictional reach imposed no measurable cost; for an operator inside Russia, doxing is a nuisance, not a deterrent, which is consistent with the ecosystem-wide conversion gap between identification and consequence. The Gentlemen continues operating under its existing brand in forum postings and on its leak site. Internal chats show discussions of OPSEC enhancements and contingency infrastructure planning, but not a structured exit strategy or rebrand timeline. [2][3]
The group's victim accumulation rate remains among the fastest documented for any RaaS program: Unit 42 measured slightly more than 6x growth comparing H2 2025 to H1 2026. In June and July 2026 The Gentlemen overtook Qilin for the monthly top position (internal collection: 118 and 136 victims against Qilin's 79 and 127; NCC Group's July count had The Gentlemen first at 138, 15 percent of all leak-site posts). Qilin retook first place in August with its best month on record (161 internal) against The Gentlemen's 115, resolving the position question as variance rather than structural displacement. The durable finding is the two-leader pattern: since May 2026, The Gentlemen and Qilin have each run at roughly double the volume of every other group, with Breachsense 2026 year-to-date counts of 893 (Qilin) and 675 (The Gentlemen) against 332 for third-placed DragonForce. [19][16]
- Encryptor under active development: Microsoft notes new defense-evasion features and self-propagation mechanics being added over time; the malware is not static. [1]
- High baseline: Multi-platform support (Windows, Linux, NAS, BSD, ESXi) from launch indicates developers began at an advanced technical level rather than iterating up from a basic ransomware. [5]
- EDR evasion maturation: Huntress and Trend Micro document adoption of custom EDR-evasion tools, tamper-protection bypasses, and increased scheduled-task abuse. ESET has since analyzed the group's dedicated EDR-killer framework, dubbed GentleKiller, and Expel reports a suspected zero-day exploit used to disable EDR products. Kaspersky documents a custom Go-based backdoor. [12][14][19]
- Self-propagation worm capability: The 21-execution-path propagation module is a significant capability differentiator; rapid network-wide encryption reduces the window for defenders to isolate and respond. [1]
| Group | Relationship | Confidence | Notes |
|---|---|---|---|
| Qilin | Parent ecosystem; founder ran Qilin affiliate crew ArmCorp, split after July 2025 payment dispute; now Qilin's only volume peer and direct competitor for affiliates | Credible (Halcyon, IBM, Ransom-ISAC, Unit 42, SOCRadar) | Distinct groups; not a rebrand. Unit 42's July 2026 profile endorses the ArmCorp affiliate origin, citing PRODAFT |
| LockBit / Black Basta (affiliate layer) | Silent Push tracks one serial affiliate via Cobalt Strike watermarks across LockBit, Black Basta, Qilin, and now The Gentlemen intrusions | Credible (Silent Push, Apr 2026) | Affiliate-level personnel continuity, not an organizational link; supports the model that people, not brands, are the durable unit |
| SystemBC ecosystem | Shared tooling; affiliates deploy SystemBC as proxy/C2 | Confirmed (shared tool), Low (structural tie) | SystemBC used across dozens of RaaS groups; not an organizational link |
| BreachForums marketplace | Official affiliate recruitment partnership | Confirmed (Microsoft, May 2026) | Supply-chain link; BreachForums provides affiliate pipeline |
| IAB ecosystem / infostealer vendors | Operational dependency; group purchases infostealer logs for credential access | Confirmed (Hudson Rock, internal chats) | Shared criminal supply chain, not organizational merger |
- Leadership identity (partially resolved June 2026): Krebs identified zeta88/hastalamuerte as Alexander Yapaev (CREDIBLE, single-outlet); no LE confirmation, and the other leaked handles remain unattributed.
- On-chain forensics: No TRM Labs, Chainalysis, or Elliptic study specifically mapping The Gentlemen's fund flows has been published. Still the largest open gap given the affiliate-owned wallet model.
- Code lineage to Qilin: Full reverse-engineering comparison between The Gentlemen encryptor and Qilin's codebase has not been publicly published.
- CrowdStrike / Secureworks designations: Neither has published a tracking designation as of September 2026. Unit 42 published a formal profile in July 2026 but assigned no codename.
- Linux / ESXi encryptor details: Kaspersky's Securelist analysis covers the C and Go variants and the Go backdoor, but deep-dives comparable to Microsoft's Windows analysis remain unpublished for the NAS, BSD, and ESXi lockers.
- Suspected EDR zero-day: Expel's reporting does not name the vulnerability; whether it is a true zero-day or an unpatched known flaw is unresolved.